
Partner programme
Vishing Simulation for MSSPs
The Callstrike partner programme lets MSSPs, MSPs and security consultancies run AI vishing and deepfake phishing simulations for the companies they look after, from one partner console, with each customer's consent and controls built in.
1
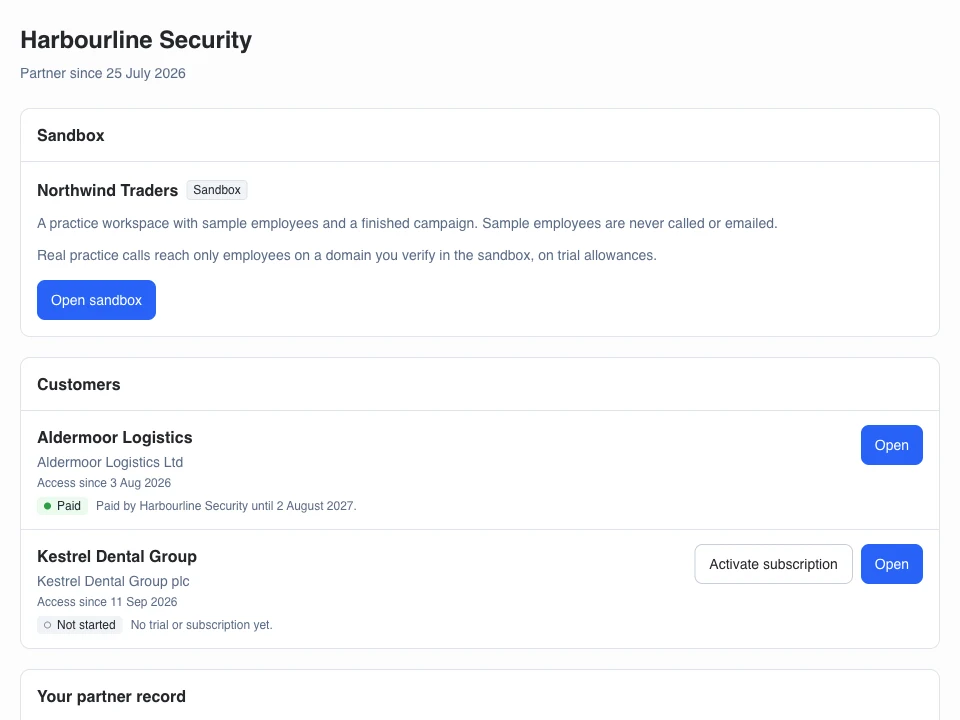
Partner console for every customer you look after
8 hrs
The longest a visit to a customer's workspace can last, each one in their audit log
9
Video channels a simulation can run on, plus the phone
Deepfake phishing simulation for MSPs and their customers
Your customers already rely on you for email security and phishing tests. The attacks reaching them now arrive by phone and on video calls: a cloned voice of the finance director, a face-swapped CEO on a Teams call, a fake help desk asking for a one-time code.
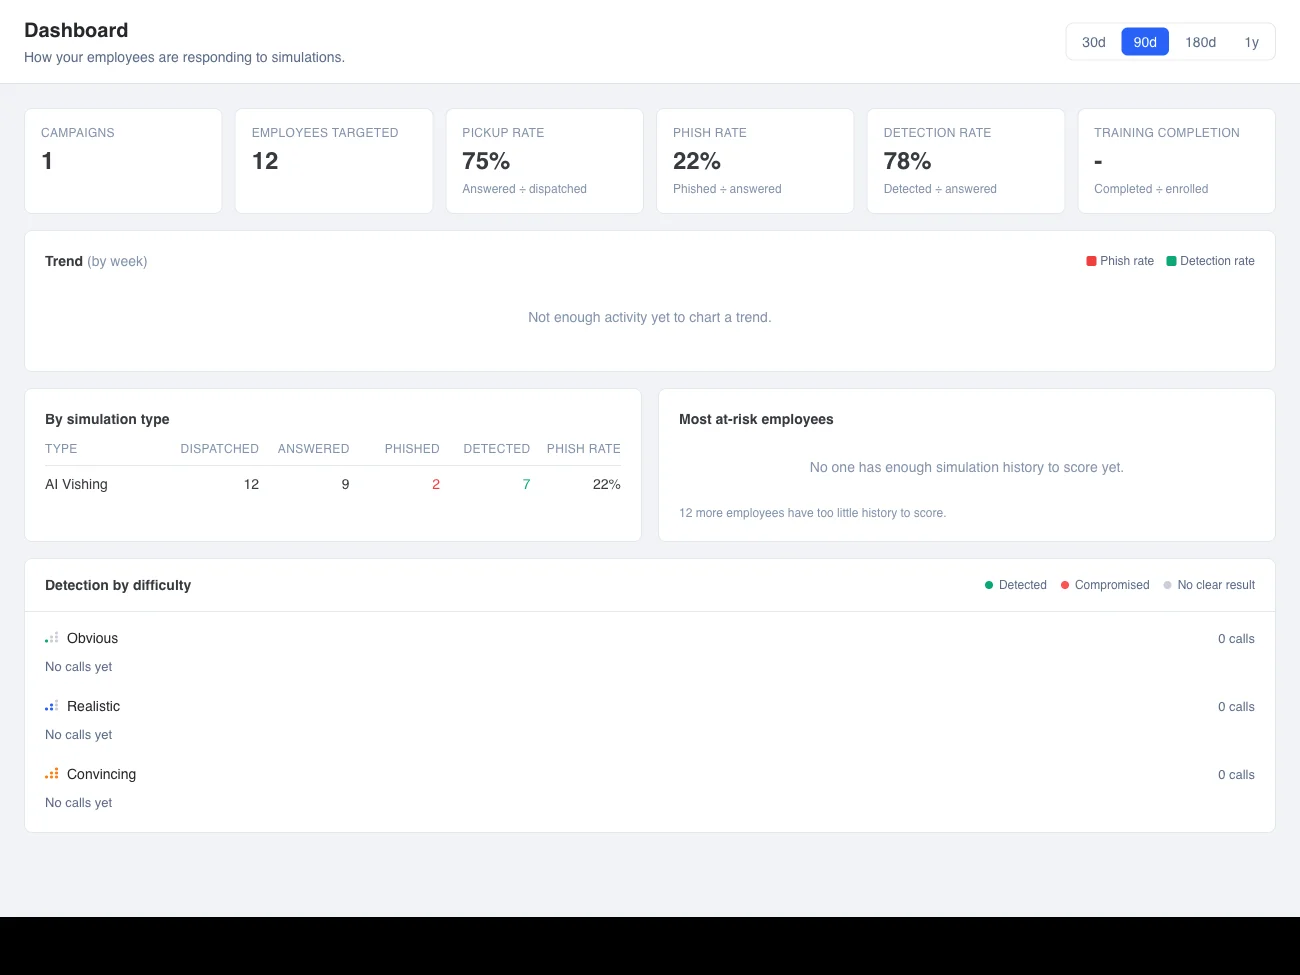
Callstrike gives you the simulations for those channels without building them yourself: AI vishing calls that hold the whole conversation, live deepfake video calls run by an operator, and results per customer that you can take into a quarterly review.
How the partner programme works
Step 1
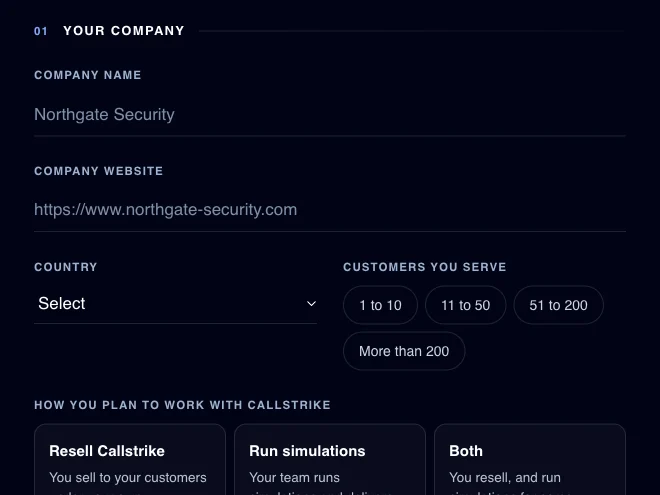
Apply and get vetted once
Tell us about your company and the customers you serve. Callstrike vets your company once, and that covers every customer you bring.
Step 2
Start in your sandbox
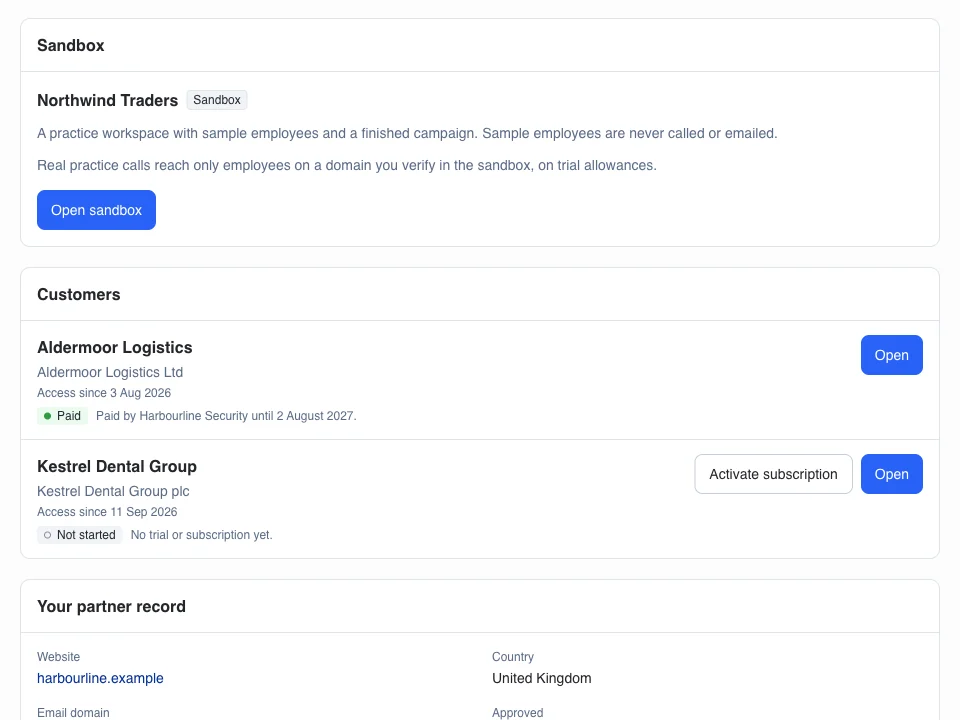
Every approved partner gets a sandbox company with sample employees who can never be called, to learn the console and demo it to prospects.
Step 3
Add your customers
Create a company for a new customer, or be given access to one that already uses Callstrike. The customer's own contact stays the owner, sees your access and can revoke it.
Step 4
Run simulations and report
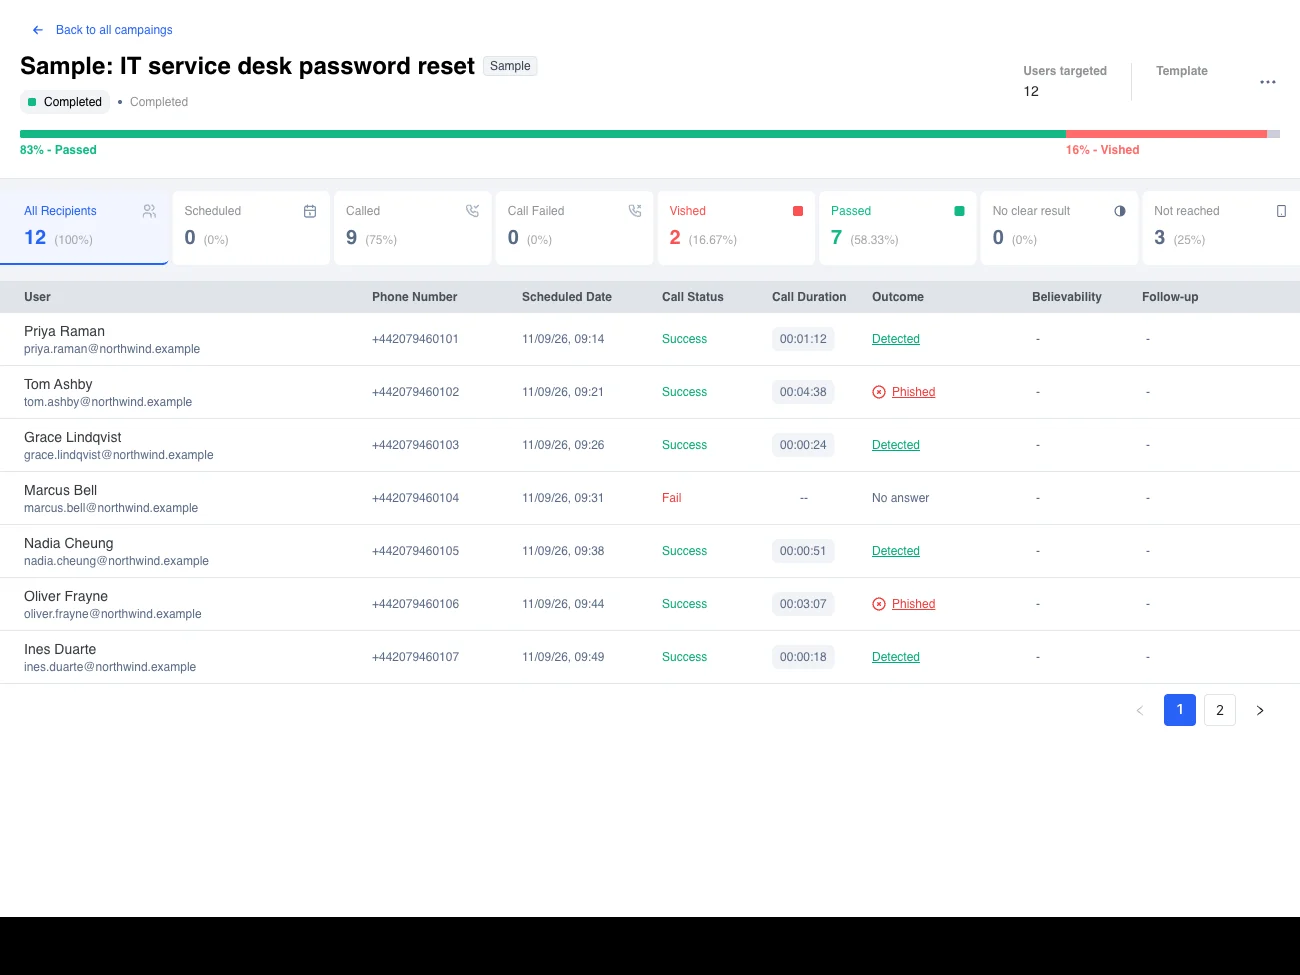
Launch vishing and deepfake campaigns as the customer's administrator, only to the customer's own employees, after they consent. Results show who complied, who refused and who reported it.
MSSP partner programme: what you get
Everything a customer of Callstrike gets, run by you, with the controls your customers' security teams will ask about.
Your brand on it
Your logo and accent colour in the partner console, your customers' workspaces and their emails, and your logo on the employees' training portal. Co-branded, so "Powered by Callstrike" stays.
Consent stays with the customer
Every employee consents before any call. You see consent counts and can chase them; you can attest consent only with the customer's signed consent document.
Every visit on the record
Each visit to a customer's workspace needs a stated reason, lasts at most eight hours and is written to the customer's audit log.
Local numbers, per country
Calls ring from local numbers bought in the customer's own details, or from the customer's own telephony account.
One bill for your customers
Callstrike bills you per customer company per year, by card or by invoice on 30-day terms. You keep the relationship and set your own price to your customer.
Built for training
Every call stops when the employee asks, and can end with in-call education, a follow-up email, or both.
Nine video channels, plus the phone
Run the exercise where the real attack would happen, for every customer.
- Phonea voice call from a local number
- Zoom
- Microsoft Teams
- Google Meet
- Slack
- Telegram
- Signal
- Webex
- GoTo Meeting
Who the partner programme is for
- Managed security service providers adding social engineering testing to a managed service.
- Managed service providers whose customers ask how to train employees against cloned voices and deepfakes.
- Security consultancies and red teams who run social engineering engagements for clients.
- Resellers who already supply security awareness training to enterprises.
See the products your customers get: AI vishing calls, deepfake video calls and human-in-the-loop voice impersonation.
Frequently asked questions
It is co-branded. Your logo and accent colour appear in the console, your customers' workspaces and emails, your logo on the training portal, and "Powered by Callstrike" stays. Sign-in pages and web addresses stay Callstrike's.
Yes. Callstrike grants your access to it. The customer's owners are emailed, see the grant in their workspace and can revoke it at any time.
Only the customer's own employees, on the customer's verified domains or domains the customer authorises in a signed letter, and only after each employee consents.
Callstrike bills the partner per customer company per year, by card or by invoice on 30-day terms. What you charge your customer is between you and them.
Most requests are reviewed within the hour. We will always come back to you within one business day.
Yes. The partner tour shows the console with a sample partner and sample customers, no sign-up needed.
Explore Related
Vishing Simulation
AI vishing calls that hold the whole conversation, from local numbers, consent first.
ProductDeepfake Phishing Simulation
Cloned voices and live deepfake video calls on Zoom, Teams, Meet and six more channels.
SolutionPenetration Testing
Deepfake-powered social engineering for red teams and consultancies.
Offer vishing and deepfake simulation to every customer you look after